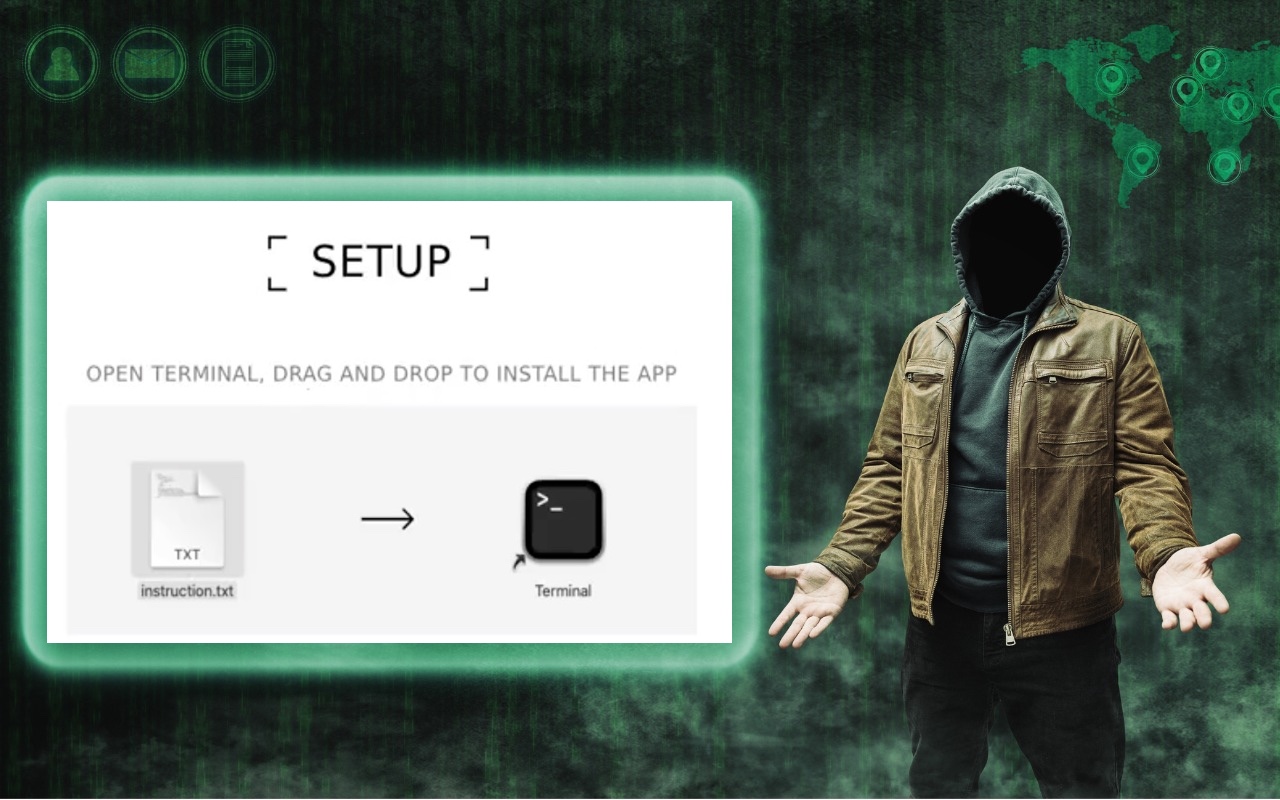
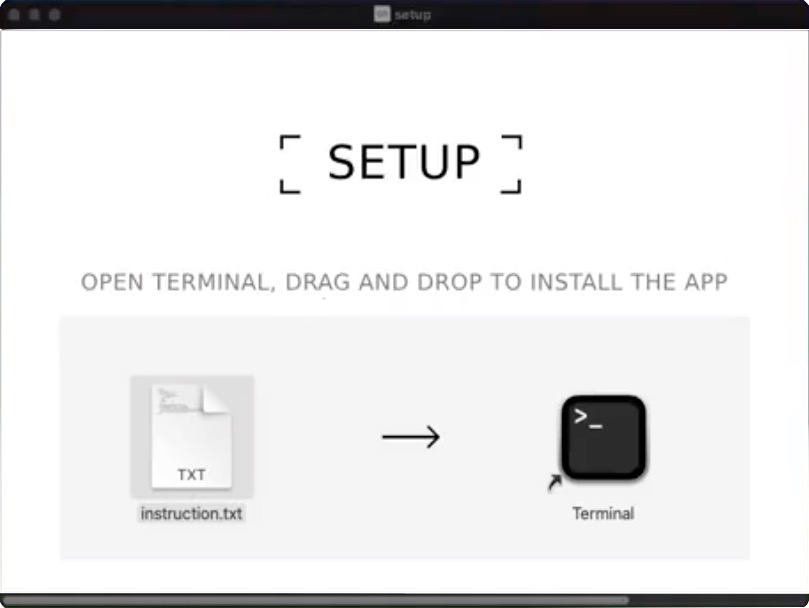
In macOS 15 Sequoia, Apple made it more difficult to bypass Gatekeeper to run apps that aren’t notarized. (Notarization is one of the ways Apple ensures that apps distributed outside the Mac App Store are unmodified and free from malware.) Cybercriminals have responded to this increase in security with a new social engineering attack—another scam. They provide the victim with a disk image, ostensibly to install some desired piece of software, instructing the user to drag a text file into Terminal. Doing so executes a malicious script that installs an “infostealer” designed to exfiltrate a wide variety of data from your Mac. The simple advice here is to treat any guidance to drop a file into Terminal with extreme suspicion—no legitimate software or developer will ever ask you to do that.
(Featured image based on an original by iStock.com/Farion_O)

A week might be too short if IT approval is still pending. I'd treat "keeping your old iPhone for a…
Awesome tech breakdown on "When Should You Upgrade to macOS 27 Golden Gate, iOS 27, iPadOS 27, watchOS 27, tvOS…
I’ve used Chrome’s built-in screenshot tool, but opening DevTools every time gets a bit tedious. I recommend FullPage Capture, it’s…
This is such an important reminder. I've been in meetings where an AI notetaker silently joined and recorded everything, and…
Awesome tech breakdown on "When Should You Upgrade to macOS 27 Golden Gate, iOS 27, iPadOS 27, watchOS 27, tvOS…